CVE-2026-98432: All affected systems patched within hours
02.11.2026 | News | Luca Albrecht
CVE-2026-98432 is a use-after-free flaw in the IPv4 TCP handshake path of the Linux kernel, affecting kernel versions 4.4 and later. A remote attacker without any credentials can trigger it by sending crafted TCP packets to a listening port, which can lead to a kernel crash, disclosure of kernel memory, or memory corruption. Researchers have already demonstrated unauthenticated remote code execution as root against hosts with a Multipath TCP listener. For an infrastructure provider like us, a critical kernel flaw means one thing: patch immediately.
When the vendor patches were released on Friday the 30th of October 2026, we did not wait. Our team started rolling out the fixes the very same evening, one system after another. There were no public reports of active exploitation at that point, but the disclosed exploit path made it clear that the window for action was short. At stepping stone AG, a critical kernel vulnerability in our infrastructure is always treated as an emergency, never as a routine update.
During the maintenance work, a brief issue in our network setup caused some of our services to be temporarily unreachable. We fixed it as soon as it became apparent, and full availability was restored shortly after. We have documented what went wrong so that it does not happen again.
This event reminded us why security sits at the center of everything we do. Speed and stability can sometimes compete with each other, but when a critical flaw like CVE-2026-98432 is on the table, there is no middle ground. We would do it exactly the same way again: patch first, report afterwards, and make sure our customers' data stays protected.
More News

02.11.2026 | News
CVE-2026-98432: All affected systems patched within hours
On Friday the 30th of October 2026, vendor patches were released for CVE-2026-98432, a critical Linux kernel vulnerability with a CVSS 3.1 score of…
27.10.2026 | Events
Retrospection on the B2B Table Football Event 2026
On Wednesday, 21 October 2026, netiva's location in Liebefeld-Bern hosted the B2B Table Football Event 2026. Once again, business met play: an evening…
26.10.2026 | News
Two critical vulnerabilities in one week: how we kept our cloud secure
Last week, two critical vulnerabilities hit the IT industry within days of each other: PwnEscape in the Linux kernel and PHP2Shell in the PHP runtime.…
22.10.2026 | News
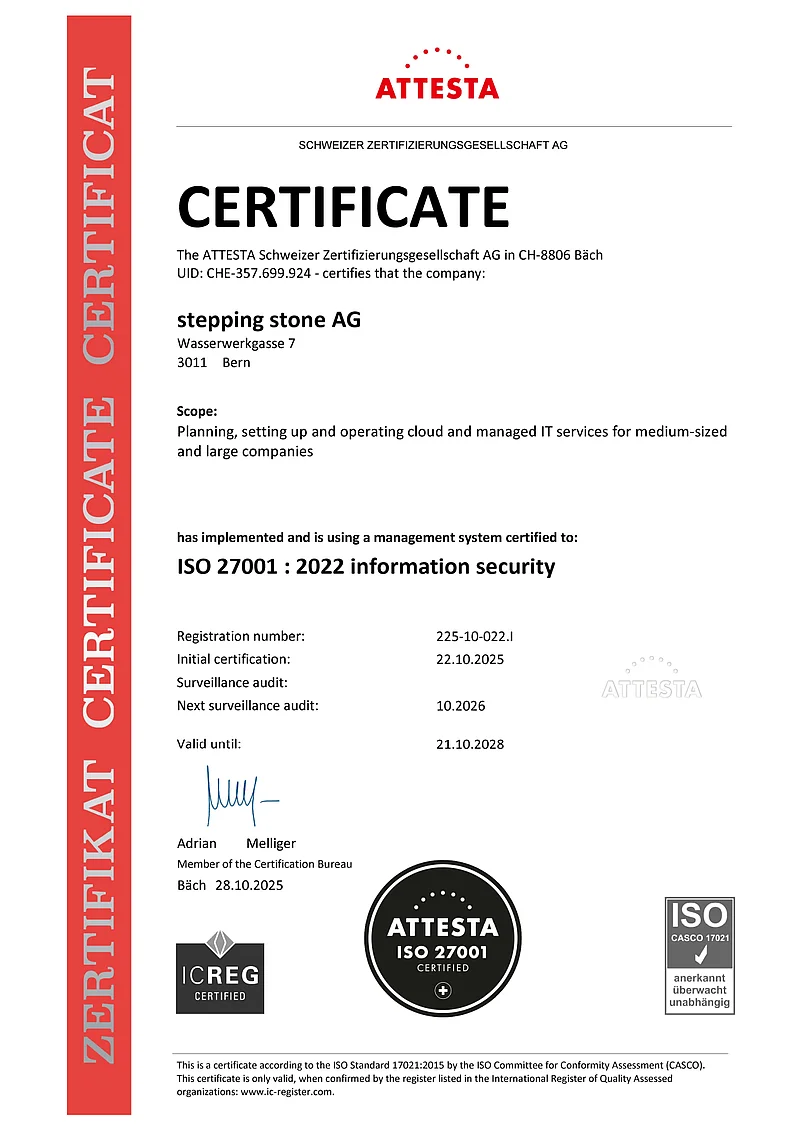
ISO/IEC 27001:2022 successfully recertified and the ISMS extended to include cloud security and data protection
On the 22nd of October 2026, we successfully completed our annual external audit. As a result, our Information Security Management System (ISMS)…
21.10.2026 | Maintenance window
PHP2Shell vulnerability: The security issue is fully mitigated across all systems
PHP2Shell is the name given by the security community to two critical vulnerabilities in PHP (CVE-2026-109618 and CVE-2026-109619). Exploiting these…
21.10.2026 | Maintenance window
PHP2Shell vulnerability: Critical security vulnerabilities in PHP, we will apply the patch as soon as it becomes available
PHP2Shell is the name given by the security community to two critical vulnerabilities in PHP (CVE-2026-109618 and CVE-2026-109619). Exploiting these…