ISO/IEC certifications
An overview of our certified standards and how they help protect both your data and our operations.
Summary
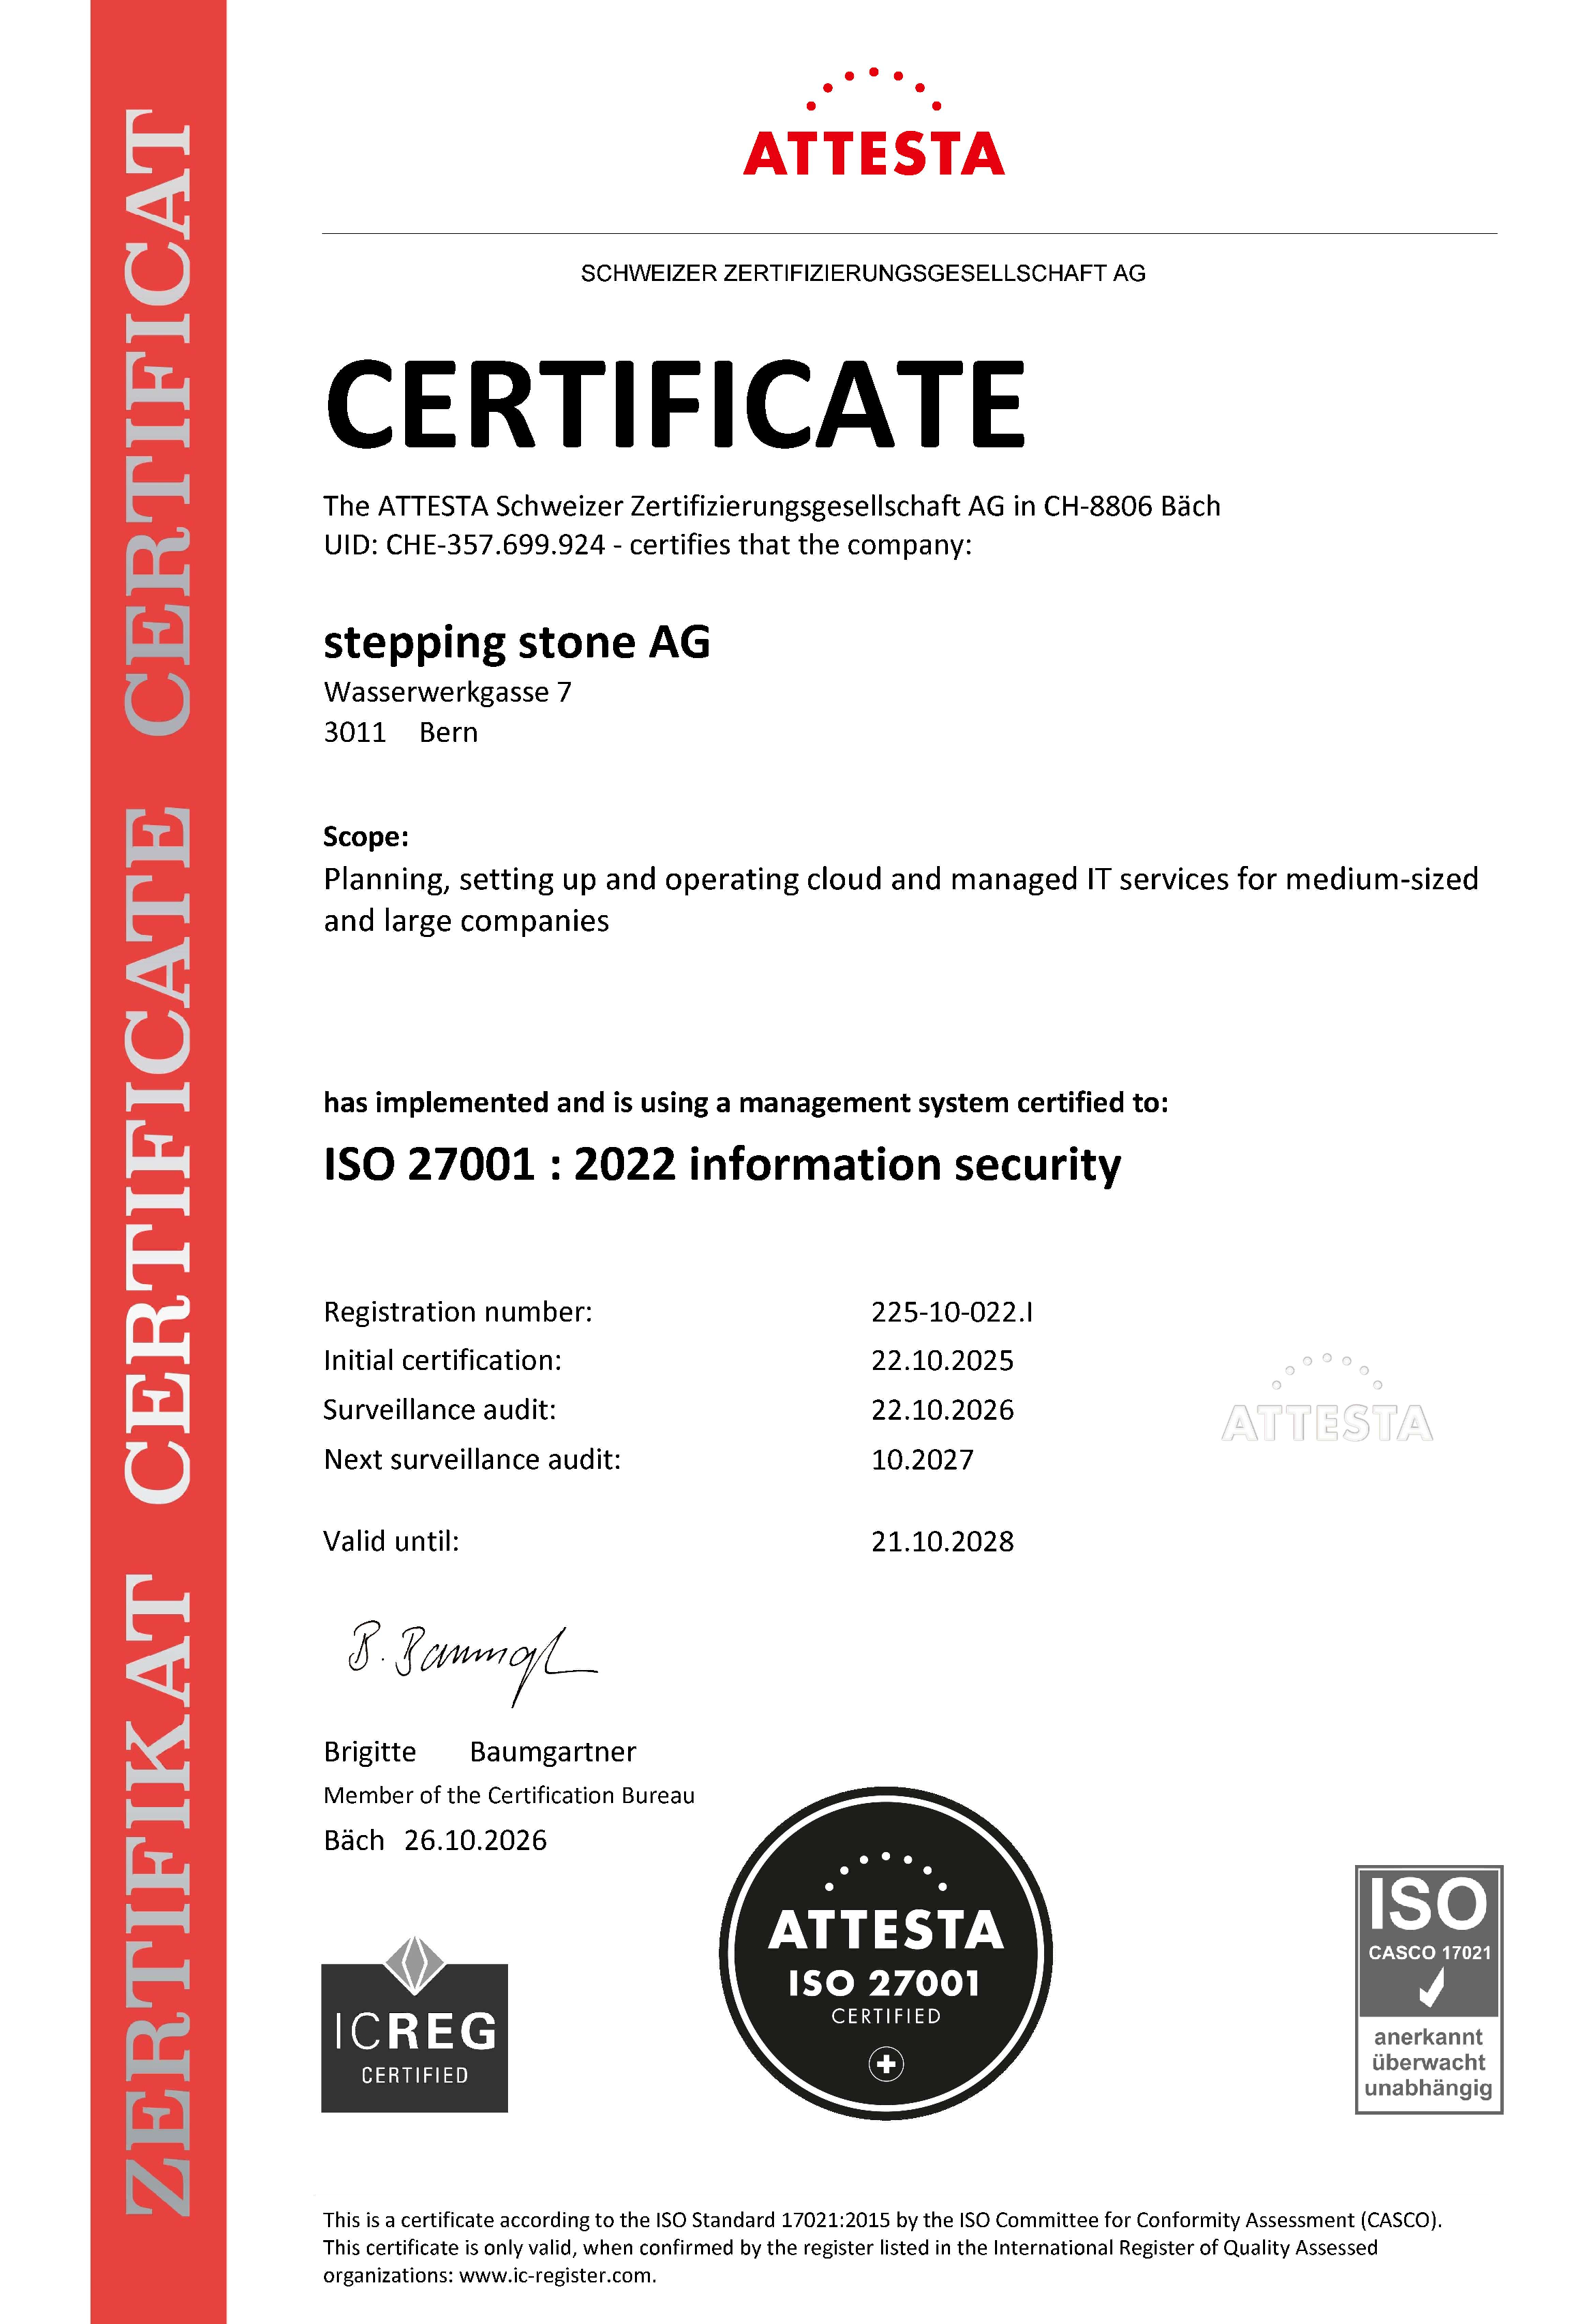
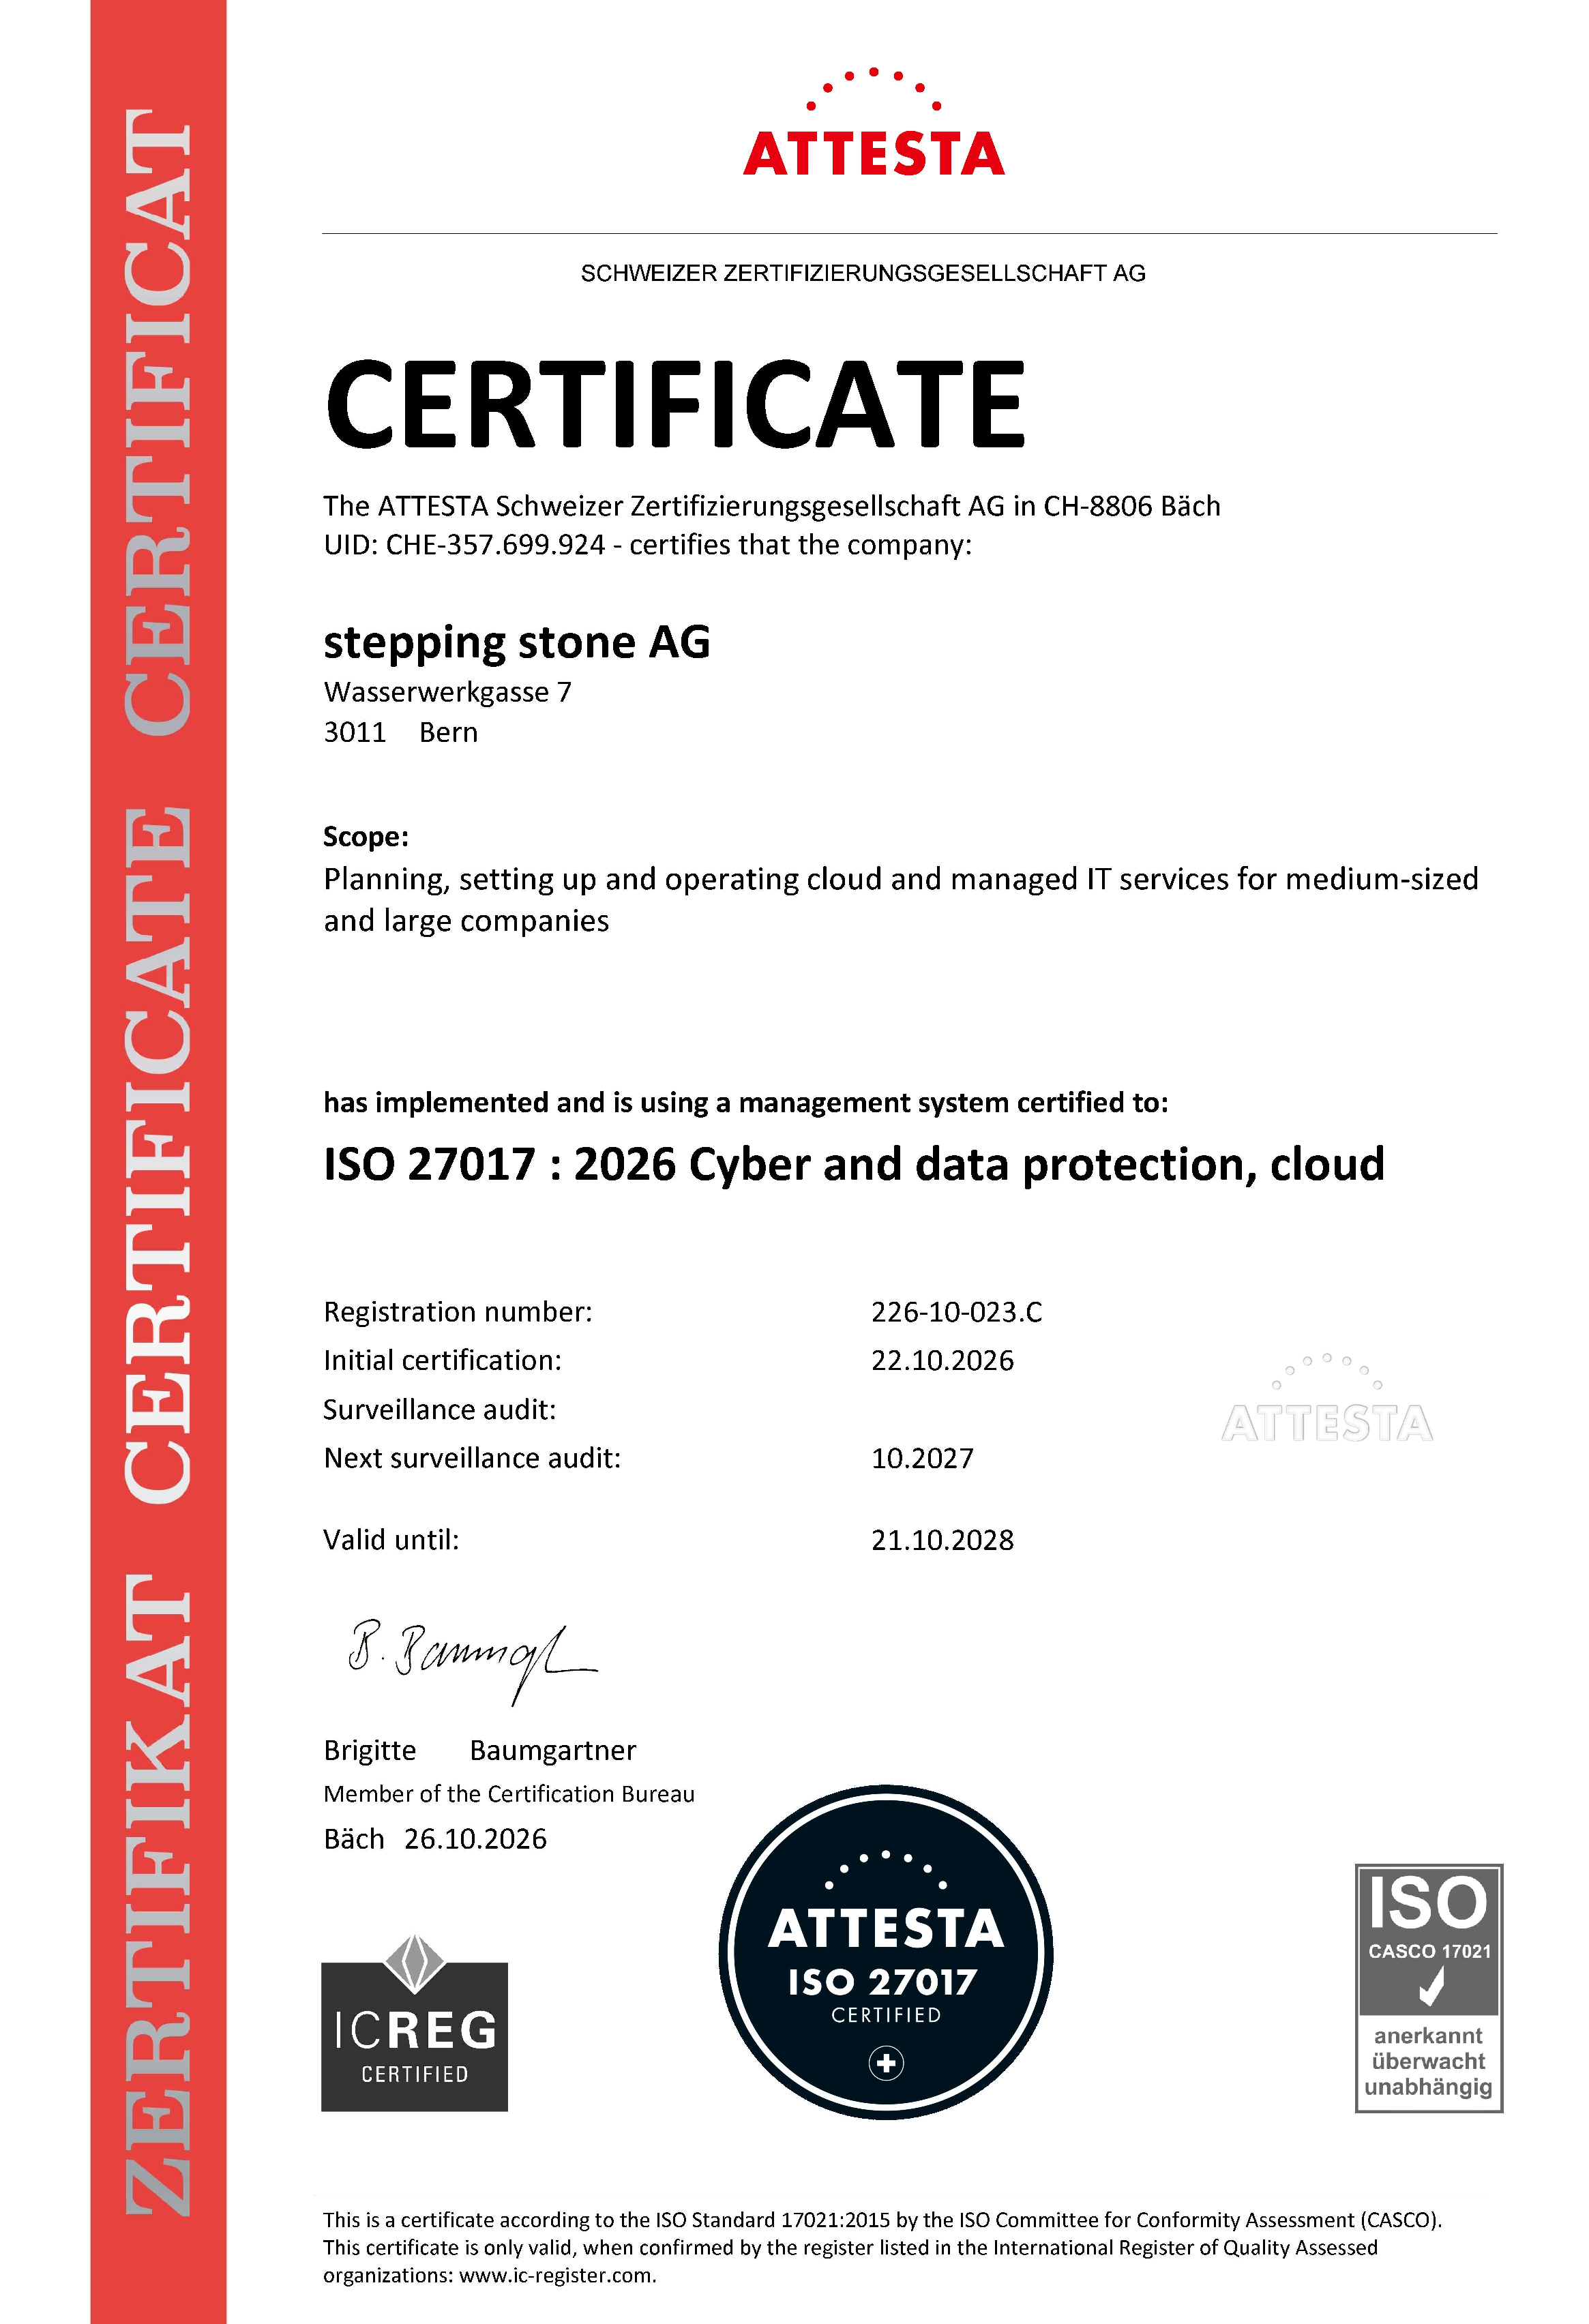
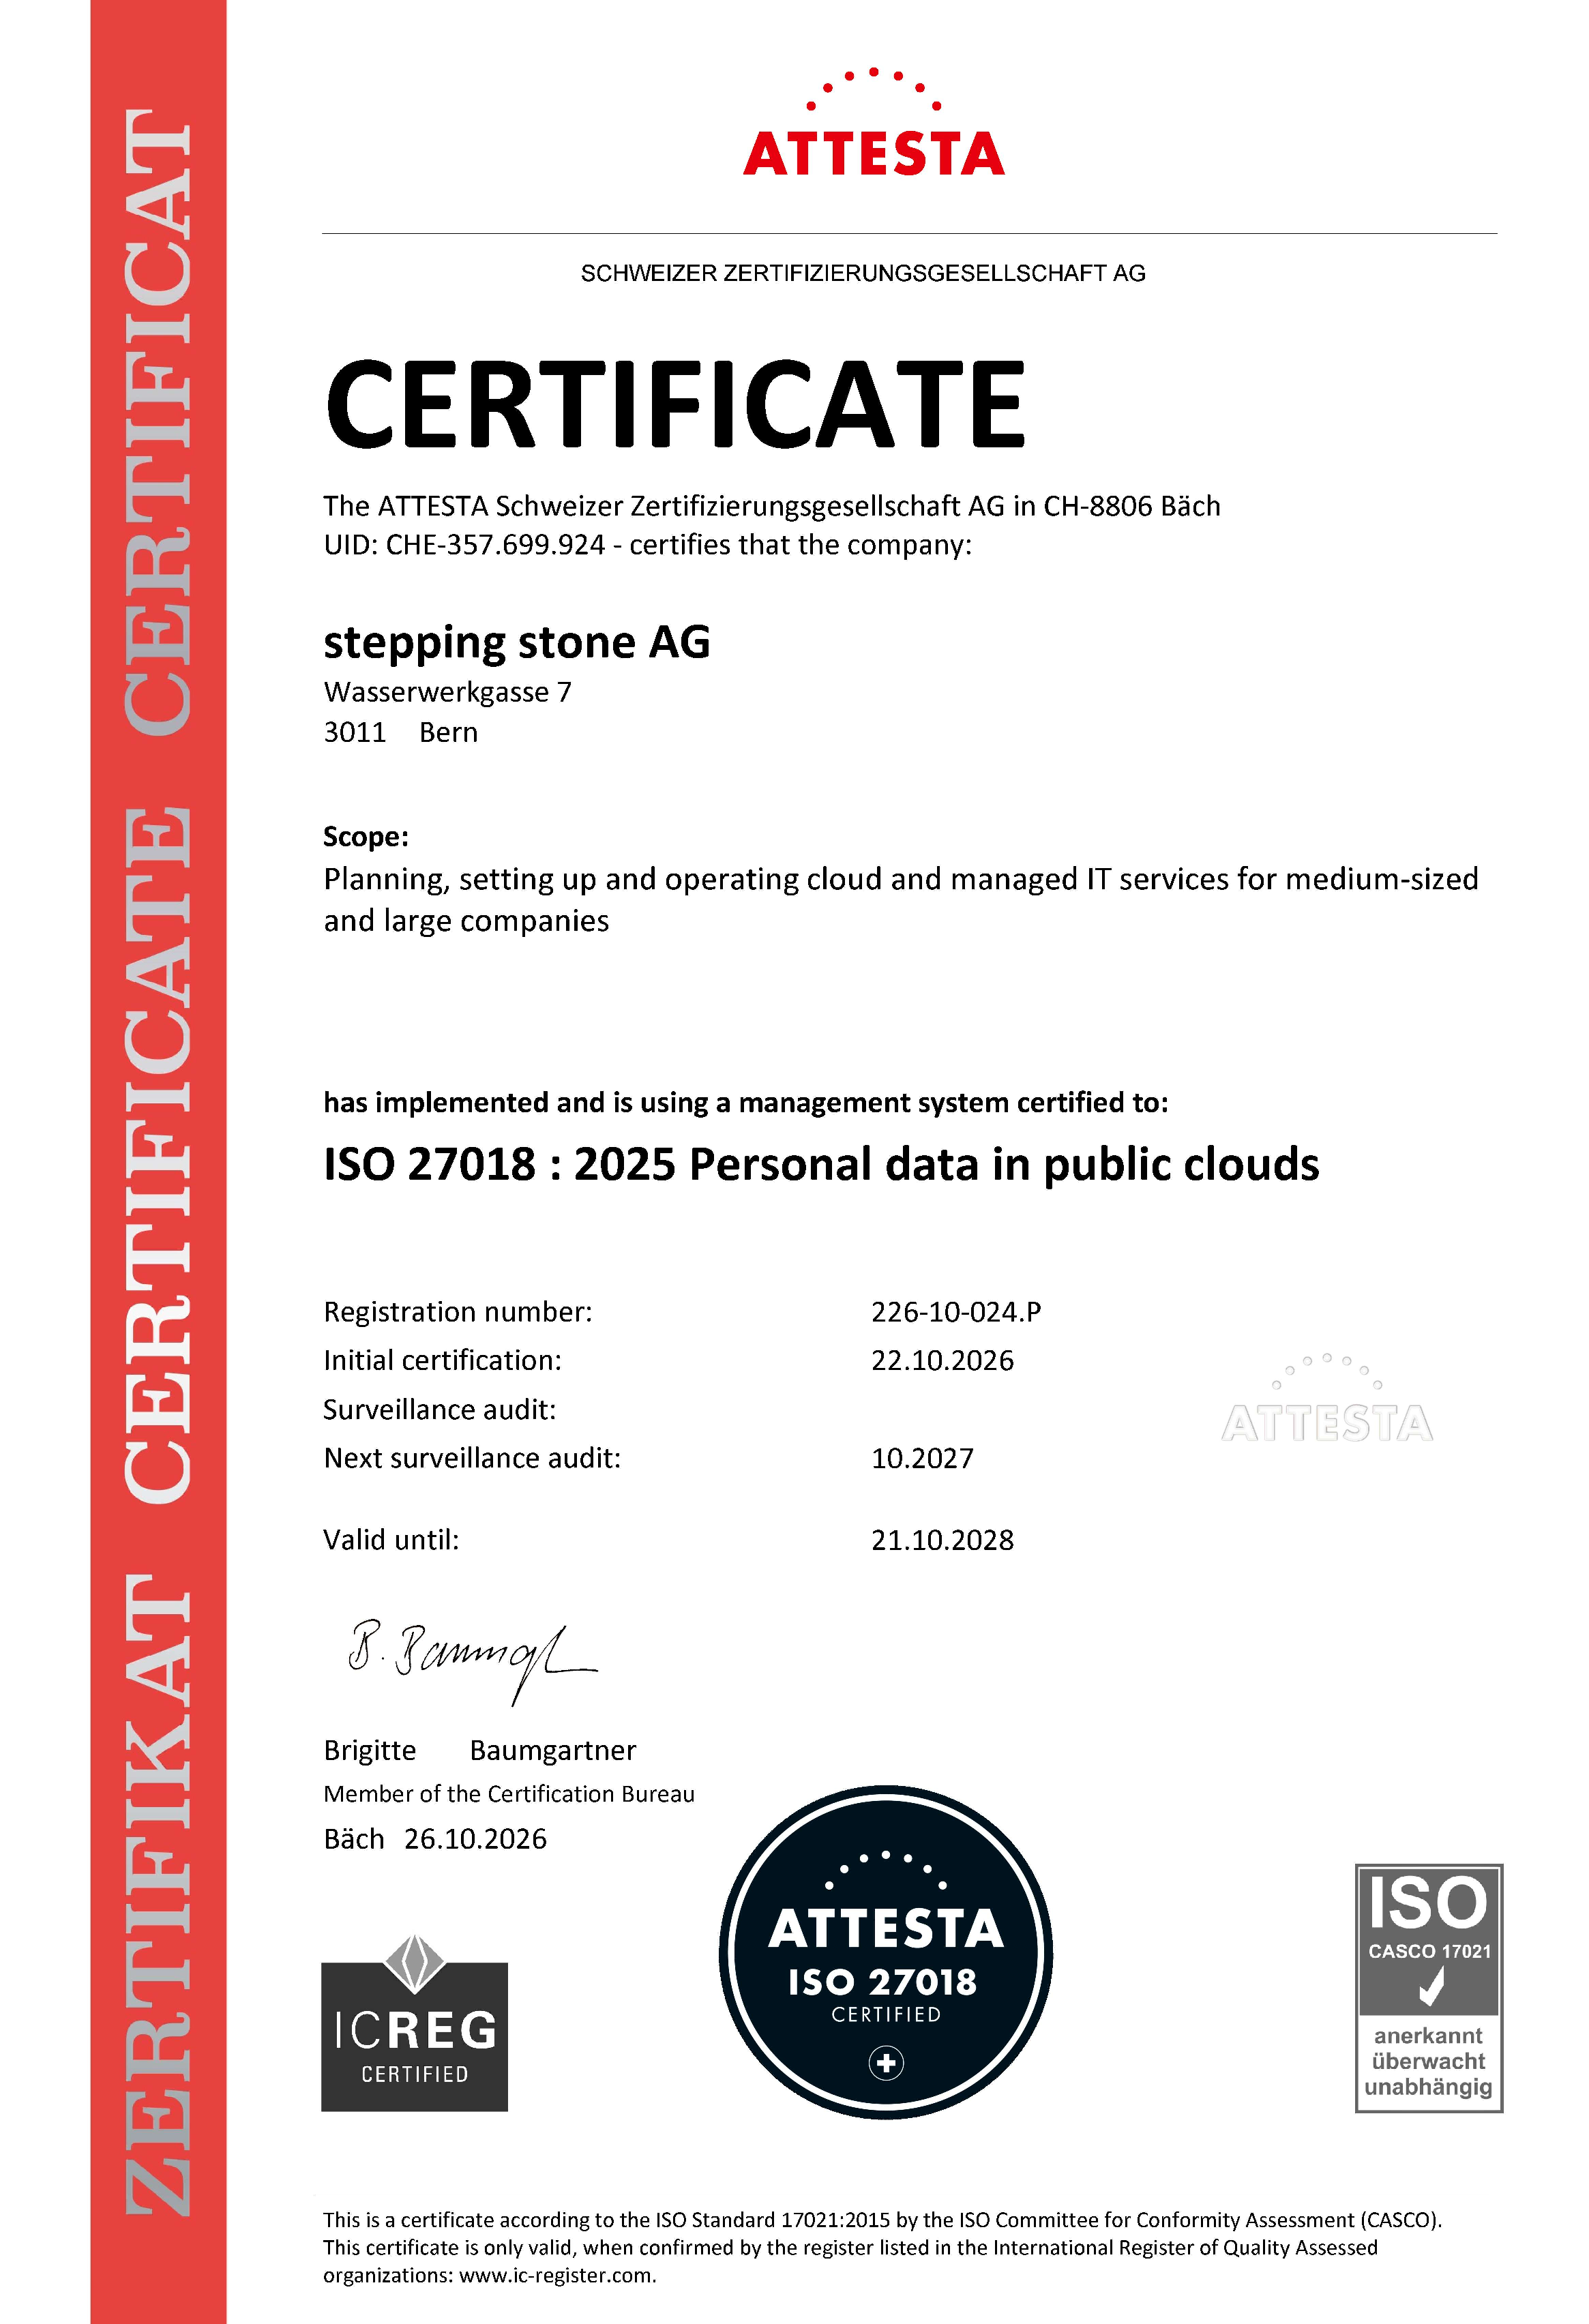
We have been certified according to ISO/IEC 27001 since October 2019. In October of 2026 we added two additions to our existing Information security management system (ISMS) with ISO/IEC 27017:2026 and ISO/IEC 27018:2025.
Specifically, the ISO/IEC certifications focus on the following key points:
- ISO/IEC 27001:2022 Information Security: The international standard for information security management systems (ISMS). It provides a framework to protect data and manage security risks.
- ISO/IEC 27017:2026 Cloud Security: Provides security controls specifically for cloud services. It guides both providers and customers in managing cloud security risks.
- ISO/IEC 27018:2025 Privacy Protection: Focuses on protecting personal data in the cloud. It establishes controls for handling personally identifiable information (PII) in public cloud environments.
Further information may be found on the official iso.org websites for ISO/IEC 27001:2022, ISO/IEC 27017:2026 and ISO/IEC 27018:2025.
Why do we rely on ISO/IEC certifications?
With the ISO/IEC certifications we commit to our customers and ourselves to the use of an information security management system (ISMS) with regular review of risks and processes. This is as important for our customers as it is for us, as it builds trust and ensures the highest security standards are always upheld. The guidelines of the information security management system (ISMS) apply to all employees of stepping stone AG, to all third parties who carry out tasks or perform services for stepping stone AG and to all customers or visitors of stepping stone AG.
By adding the two new add-ons ISO/IEC 27017:2026 and ISO/IEC 27018:2025 we have shown that we are eager to ensure full compliance with best practices for protecting personal data in the cloud. This becomes more important every day in a digital world where sensitive data is constantly at risk.
Certifications
Together with our internal auditors at Redguard AG and our external auditors at ATTESTA Schweizer Zertifizierungsgesellschaft AG, we conduct annual audits to review and strengthen our processes, ensuring full compliance with the ISO/IEC certifications and preserving the integrity of our standards.
You can find the most recent certifications below.